New Spectre-derived timing attack targets modern Intel and AMD CPUs
Researchers at MIT's Computer Science and Artificial Intelligence Laboratory (CSAIL) have revealed a new Spectre-style timing vulnerability dubbed TONTOU (Time-of-Neutralization to Time-of-Use) that can bypass recent hardware defenses introduced by Intel and AMD. The discovery highlights ongoing risks posed by speculative execution flaws and their potential impact on hardware security in cloud and crypto infrastructure.
What is TONTOU and how does it work?
TONTOU leverages a tiny timing gap between when a CPU neutralizes speculative predictions and when the processor actually uses speculative execution results. Modern CPUs rely on speculative execution to improve performance: the processor predicts future code paths and executes them ahead of time. If the prediction is wrong, results are discarded, but residual microarchitectural traces—such as cache state—can leak information to attackers via side-channel techniques.
After the original Spectre disclosures in 2018, chipmakers introduced mitigations designed to clear or isolate speculative state before executing sensitive code. MIT researchers found that neutralization (the clearing step) and the moment of actual use are not always perfectly synchronized. TONTOU exploits that short window to reintroduce malicious data into the prediction path and recover information through microarchitectural side channels.

Platforms tested and real-world feasibility
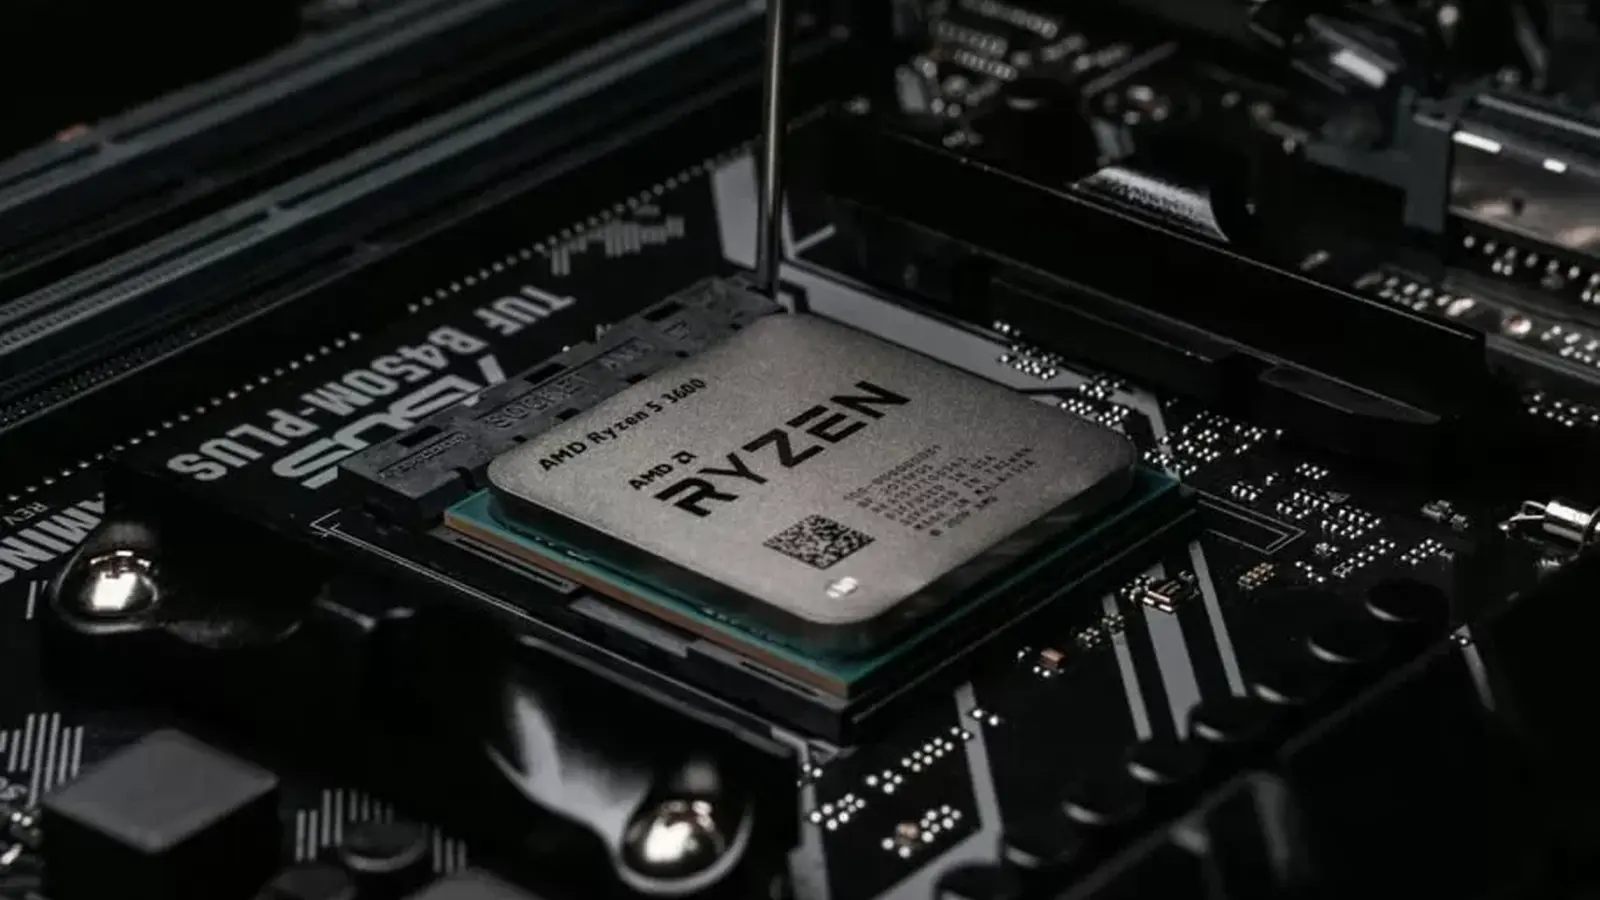
The team tested TONTOU on Intel processors (Cascade Lake Refresh and Arrow Lake) and AMD microarchitectures (Zen 2 and Zen 4). They were able to trigger mispredictions on both vendors' platforms. In AMD's Safe RET defense, the exploitable window is extremely small—just two instructions—but careful timing control made the attack possible.
On an AMD Zen 2 system running an unmodified Linux kernel, researchers executed a full proof-of-concept exploit that successfully defeated KASLR (Kernel Address Space Layout Randomization) in every run across 10 attempts. However, practical constraints limit widespread abuse: measured read speed was roughly 5 bytes per second, and each full exploit attempt took about 18 minutes. Intel targets require specific software conditions to succeed. For these reasons, TONTOU is not currently an easy vector for commodity malware on consumer PCs.
Implications for cryptocurrency and blockchain systems
Although TONTOU's throughput and latency make mass exploitation difficult, the attack is significant for high-value targets common in the crypto space. Hardware wallets, validator nodes, cloud-based mining rigs, and servers storing private keys or seed material could be attractive targets for sophisticated attackers. Side-channel attacks that leak private keys or KMS secrets could directly threaten custodial services, exchanges, and staking infrastructure. Operators should treat CPU microarchitectural vulnerabilities as a real threat to blockchain security.
Mitigation and responsible disclosure
MIT researchers informed AMD and Intel in February and contacted Linux kernel maintainers in March. AMD has already released a Linux kernel patch to address the vulnerability; users and administrators should prioritize updating kernel packages and following vendor firmware advisories. Additional mitigations include avoiding untrusted code execution on shared hosts, isolating critical workloads, and applying recommended microcode and OS updates.
As speculative-execution side channels continue to evolve, organizations—especially those handling cryptocurrency private keys and high-value blockchain services—must maintain rigorous patching practices and hardware threat models. While TONTOU is not an immediate threat to average desktop users, it underscores the persistent importance of hardware security and timely updates for both cloud and crypto ecosystems.

Leave a Comment
Comments
No comments yet. Be the first.